China's NMPA Launches Full Coverage Inspections for Medical Institutions
Time
Click Count
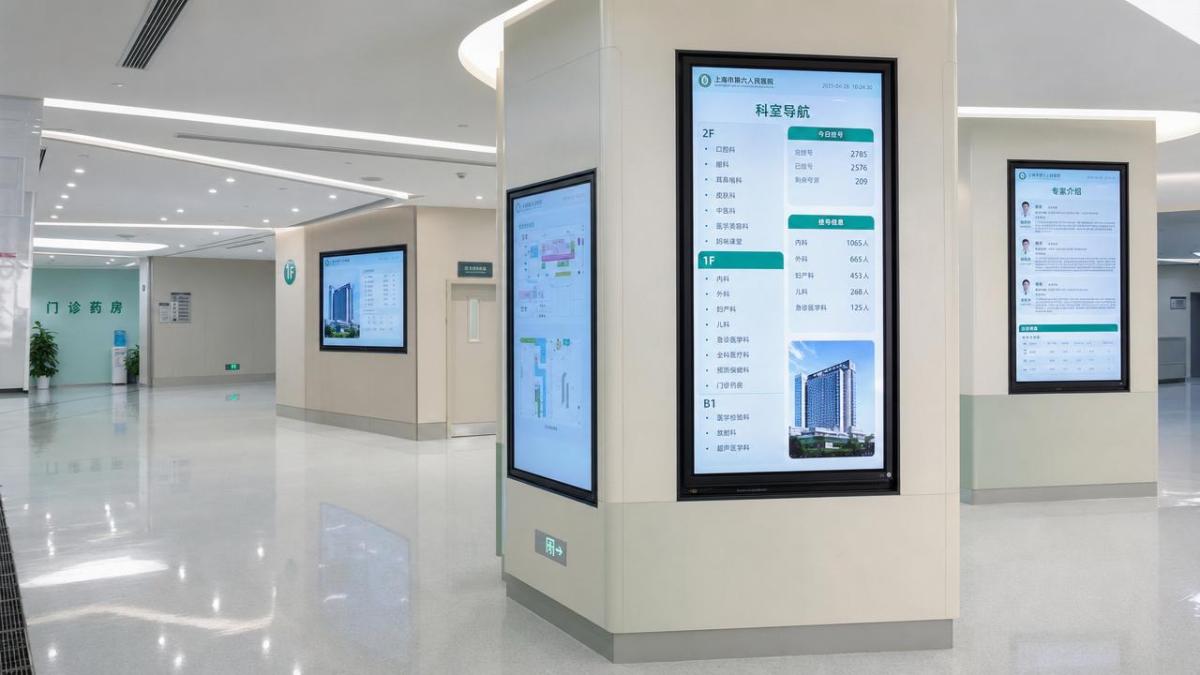
On May 13, 2026, China’s National Medical Security Administration (NMSA) launched a nationwide regulatory initiative targeting all designated medical institutions and pharmacies — marking a pivotal shift in compliance expectations for digital health infrastructure. The move directly impacts vendors of digital signage and wayfinding systems used in healthcare settings, as the newly introduced inspection criteria now include technical interoperability requirements previously unenforced at scale.
Event Overview
On May 13, 2026, the NMSA issued the Five-Year Action Plan for Medical Security Fund Supervision and Inspection (2026–2030). The plan mandates full on-site inspections of all designated medical institutions and pharmacies across China during the 15th Five-Year Plan period (2026–2030). A newly added inspection item — ‘compliance of intelligent wayfinding device data interfaces’ — requires that Digital Signage Solutions must support GB/T 38671-2026 (a national standard for healthcare information exchange) and achieve bidirectional integration with Hospital Information Systems (HIS), including audit log retention of ≥180 days. Non-compliant systems will be excluded from the national medical insurance settlement supporting procurement list.
Industries Affected
Direct Trading Enterprises
Enterprises engaged in distribution or reselling of digital signage hardware and software to hospitals face immediate commercial risk. As inclusion in the NMSA’s approved procurement list becomes a de facto prerequisite for hospital tenders, distributors lacking certified, compliant solutions may lose access to public-sector contracts — especially in tier-2 and tier-3 cities where procurement decisions heavily reference national eligibility criteria.
Raw Material Procurement Enterprises
Suppliers of core components — such as embedded controllers, secure communication modules, or certified display panels — are indirectly affected. Demand is shifting toward components pre-validated for GB/T 38671-2026 conformance and capable of supporting long-term, tamper-resistant logging. Procurement cycles may lengthen as integrators require traceable compliance documentation, increasing pressure on upstream suppliers to obtain third-party certification.
Manufacturing Enterprises
OEM/ODM manufacturers of medical-grade digital signage must now embed protocol stacks, encryption layers, and HIS-integration middleware into firmware — moving beyond basic display functionality. This raises R&D costs and extends time-to-certification. Firms without in-house healthcare IT expertise may need to partner with HIS vendors or middleware providers to meet the bidirectional log retention requirement.
Supply Chain Service Providers
Logistics, installation, and post-deployment validation service providers face new scope requirements. On-site commissioning now includes interface handshake testing, HIS log synchronization verification, and documentation of 180-day retention capability — tasks requiring trained healthcare IT technicians rather than general AV installers. Certification of service personnel and standardized audit checklists are likely to become contractual prerequisites.
Key Focus Areas and Recommended Actions
Verify GB/T 38671-2026 Implementation Depth
Compliance is not limited to syntactic adherence (e.g., message format); it requires semantic interoperability — including correct mapping of clinical location codes, real-time bed status feeds, and emergency routing triggers. Vendors should conduct end-to-end conformance testing with major HIS platforms (e.g., Kingdee Health, Yonyou Healthcare, iSoftstone MedIT).
Audit Log Architecture Must Meet Retention & Integrity Requirements
The ≥180-day log retention mandate applies specifically to bidirectional interface events — not general system logs. Logs must be immutable, timestamped with NTP-synchronized clocks, and stored in encrypted, write-once storage (or equivalent WORM configuration). Cloud-based logging is permissible only if hosted within mainland China and compliant with PIPL data residency rules.
Prepare for Tiered Certification Pathways
While the NMSA has not yet published a formal certification body list, provincial medical security bureaus have begun piloting pre-audit assessments. Early engagement with provincial-level testing centers — particularly those affiliated with the China Academy of Information and Communications Technology (CAICT) — is advised to anticipate regional interpretation differences.
Editorial Perspective / Industry Observation
Observably, this regulation signals a structural pivot: from viewing digital signage as passive infrastructure to treating it as an auditable node in the medical security data chain. Analysis shows that the inclusion of interface logging — not just functionality — reflects growing concern over claims fraud linked to misrouted patients or falsified service records. From an industry perspective, the rule is less about hardware upgrades and more about embedding governance-by-design into health IT procurement. Current implementation patterns suggest most existing deployments lack HIS bidirectionality; retrofitting will require both technical re-engineering and institutional process alignment — meaning full compliance may lag behind the inspection rollout by 12–18 months in practice.
Conclusion
This policy does not merely raise a technical bar — it redefines the role of digital wayfinding in China’s healthcare ecosystem. It shifts market value from visual design and hardware durability toward verifiable data integrity, system accountability, and regulatory traceability. For the sector, the longer-term implication is consolidation: smaller vendors unable to absorb certification costs or sustain audit-ready operations may exit or merge, while firms with embedded healthcare IT capabilities gain defensible advantage. A rational observation is that compliance will become a baseline expectation — not a differentiator — by 2028.
Source Attribution
Official source: National Medical Security Administration (NMSA), Five-Year Action Plan for Medical Security Fund Supervision and Inspection (2026–2030), released May 13, 2026. GB/T 38671-2026 was published by the Standardization Administration of China (SAC) on March 22, 2026. Note: Provincial implementation guidelines, certification timelines, and authorized testing laboratories remain pending — these elements warrant continuous monitoring over Q3–Q4 2026.
News Recommendations
 Report: Global Kraft Paper Market Forecast to Reach $20.5 Billion by 2033
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to verify Zigbee compatibility when sourcing lighting sensors
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How do packaging customization options affect minimum order quantities in Europe?
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 Transom to Acquire Cree LED in Commercial Lighting Ownership Change
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to plan customer flow in commercial design planning
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 USTR Urged to Permanently Suspend Fees on China-Linked Ships
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to choose comparable stores for retail benchmarking
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How does anchoring affect modular building wind load resistance?
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 Amazon Raises European FBA Surcharge to 2% in Ten Markets From November 2
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to verify a BPA-free test report for baby products
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 China's Mandatory Classroom Lighting Standard GB 7793-2025 Takes Effect November 1
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How order volume affects the price of wholesale poly mailers
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 US Imposes 50% Tariff on Certain Canadian PET Resin Imports
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to read the maximum ratings in a semiconductor datasheet
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 University of Maryland Develops Bio-Based Packaging to Extend Avocado and Cucumber Shelf Life
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to verify a cookware manufacturer's induction compatibility claims
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 Omdia Forecasts 11.6% Annual Growth in LED Display Revenue Through 2030
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to verify a pulp molding packaging factory's production capacity
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 Curion Survey: Half of Consumers Frustrated by Sustainable Packaging
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to assess the credibility of market insight content
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 US Removes 50% Additional Tariff on Selected Canadian Packaging Products
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 Will a waterproof dimmable LED driver work with your existing dimmer?
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 Charter Next Generation Raises Film PCR Use 30%, Advances Food-Grade Applications
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to choose a dog harness and leash for a dog that pulls hard
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to respect local customs when negotiating with overseas suppliers
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 RFID Recycling Challenges Bring Paper-Based and Chipless Tags Into Focus
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to choose commercial lighting for offices that reduces glare
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 Queue Launches Fully Automated Robotic Pharmacy Kiosk for 30-Second Dispensing
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 Can your supermarket store fixtures supplier meet your opening date?
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 Shopify POS UI Extensions 2026-10 Adds Virtual Lists and Custom Row Templates
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to assess smart office furniture suppliers’ North American support
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 Aqara Launches Smart Lighting Range to Advance AI Spatial Intelligence
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to assess demand forecasts in a lighting intelligence report
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 Billerud推出PharmaKraft纤维基医药包装材料
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to assess supplier reliability in global supply chain sourcing
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 Omdia Forecasts 11.6% CAGR for Global LED Video Display Market in 2026–2030
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to verify an LFGB testing laboratory's accreditation scope
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 How to assess a workplace interior supplier's installation scope
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings
 What records are needed for an ISO 9001 furniture factory audit?
![51a6ab95581761cc26f4318be6520c15]()
Aris Katos
Future of Carbide Coatings